Cipher Block Chaining (CBC) Mode Of Operation
Category: CRYPTOGRAPHY | 6th October 2026, Tuesday
Introduction
Cipher Block Chaining (CBC) Is One Of The Classical modes Of Operation For Block Ciphers. It Allows A Block Cipher Such As The Advanced Encryption Standard (AES) To Securely Encrypt Messages That Are Longer Than A Single Fixed-size Block. Instead Of Encrypting Every Plaintext Block Independently, CBC Connects, Or chains, Successive Plaintext Blocks Together. This Chaining Mechanism Makes The Encryption Of One Block Dependent On The Previous Ciphertext Block.
CBC Was Introduced To Overcome Important Weaknesses Associated With Directly Applying A Block Cipher Independently To Each Block. For Example, When Electronic Codebook (ECB) Mode Is Used, Identical Plaintext Blocks Produce Identical Ciphertext Blocks When The Same Key Is Used. This Can Reveal Patterns In Structured Data. CBC Reduces This Problem By Combining Each Plaintext Block With The Previous Ciphertext Block Before Encryption.
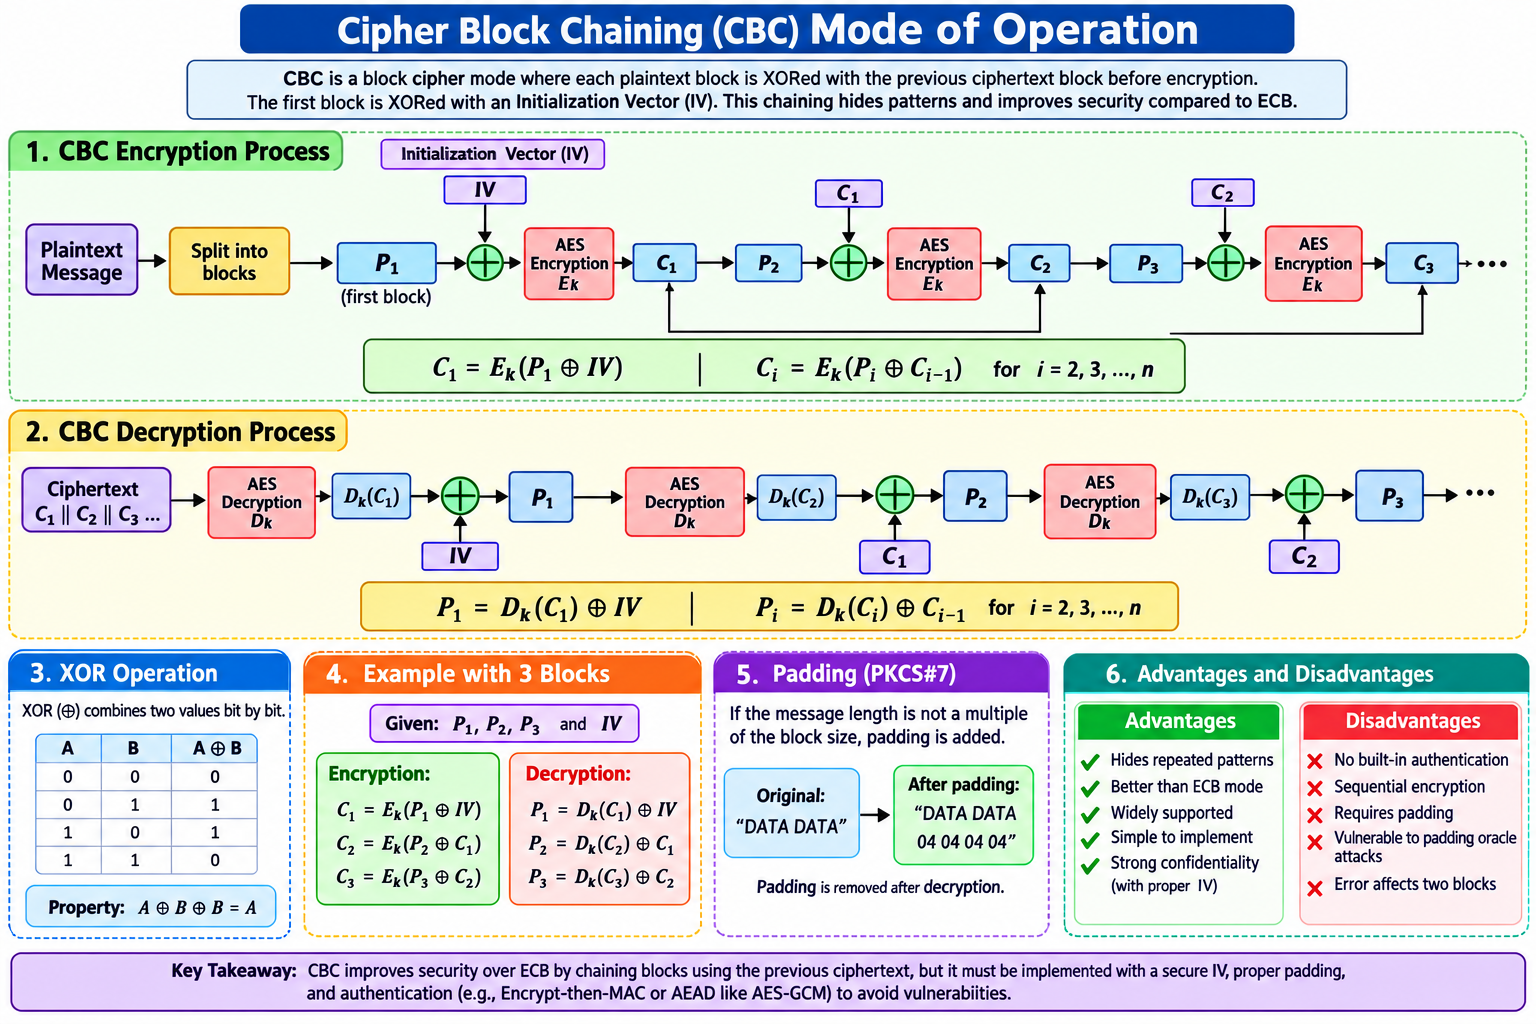
The Fundamental Operation Of CBC Is Simple. The First Plaintext Block Is XORed With An Initialization Vector (IV), And The Result Is Encrypted Using The Secret Key. Every Subsequent Plaintext Block Is XORed With The Ciphertext Of The Previous Block Before Encryption. During Decryption, The Reverse Process Is Performed Using The Same Key And The Corresponding Previous Ciphertext Block.
What Is CBC?
Cipher Block Chaining (CBC) Is A Block-cipher Mode In Which Each Plaintext Block Is Combined With The Preceding Ciphertext Block Using The XOR Operation Before Being Encrypted.
Suppose A Plaintext Message Is Divided Into Blocks:
P?, P?, P?, ..., P?
The Corresponding Ciphertext Blocks Are:
C?, C?, C?, ..., C?
CBC Encryption Can Be Represented As:
C? = E?(P? ⊕ IV)
and For Subsequent Blocks:
C? = E?(P? ⊕ C???)
where:
-
P? = Plaintext Block
-
C? = Ciphertext Block
-
E? = Block-cipher Encryption Using Key K
-
IV = Initialization Vector
-
⊕ = XOR Operation
-
K = Secret Encryption Key
Thus, CBC Introduces A Dependency Between Neighboring Blocks.
Why CBC Was Developed
A Basic Block Cipher Operates On A Fixed-size Block. For Example, AES Operates On 128-bit Blocks, While Older DES Operates On 64-bit Blocks. Real-world Messages Are Normally Much Longer Than One Block.
One Simple Solution Is To Divide The Message Into Blocks And Encrypt Each Block Independently. This Is Essentially The Idea Behind ECB Mode.
However, ECB Has An Important Weakness: Identical Plaintext Blocks Generate Identical Ciphertext Blocks Under The Same Key. Consequently, Repeated Structures Can Remain Visible.
CBC Addresses This Problem By Incorporating The Previous Ciphertext Into The Encryption Of The Current Plaintext. Therefore, Even If Two Plaintext Blocks Are Identical, Their Ciphertext Blocks Can Be Different Because Their Preceding Ciphertext Blocks Are Different.
Basic CBC Architecture
The CBC Encryption Process Can Be Represented As:
             Initialization Vector
                       |
                       V
P1 ---------> XOR ---------> AES Encryption -----> C1
               ^
               |
              IV

P2 ---------> XOR ---------> AES Encryption -----> C2
               ^
               |
              C1

P3 ---------> XOR ---------> AES Encryption -----> C3
               ^
               |
              C2
The Important Feature Is The feedback Relationship.
The Ciphertext Generated From One Block Becomes An Input To The Encryption Of The Next Plaintext Block.
Therefore:
P? → C? → C? → C? → ...
This Is Why The Technique Is Called Cipher Block Chaining.
CBC Encryption Process
CBC Encryption Begins By Dividing The Plaintext Into Fixed-size Blocks.
For AES-CBC, Every Block Is 128 Bits.
Suppose A Message Consists Of:
P?, P?, P?, P?
The Encryption Process Is:
First Block
The First Plaintext Block Is XORed With The IV:
X? = P? ⊕ IV
Then:
C? = E?(X?)
Second Block
The Second Plaintext Block Is XORed With The First Ciphertext:
X? = P? ⊕ C?
Then:
C? = E?(X?)
Third Block
X? = P? ⊕ C?
Then:
C? = E?(X?)
Fourth Block
X? = P? ⊕ C?
Then:
C? = E?(X?)
This Continues Until All Plaintext Blocks Have Been Encrypted.
Initialization Vector
The Initialization Vector, Commonly Called The IV, Is An Important Component Of CBC.
For The First Block, There Is No Previous Ciphertext Block. Therefore, CBC Uses The IV In Place Of The Previous Ciphertext.
The First Encryption Operation Is:
C? = E?(P? ⊕ IV)
The IV Should Generally Be unpredictable And Unique For Encryption. It Does Not Normally Need To Be Secret, So It Can Be Transmitted Or Stored Alongside The Ciphertext.
For AES-CBC, The IV Must Be Exactly 128 Bits, Matching AES's Block Size.
An Important Security Principle Is That The IV Must Not Be Reused With The Same Key In Situations Where CBC's Security Assumptions Require Unpredictability. Predictable Or Reused IVs Can Enable Attacks That Reveal Relationships Between Plaintexts.
XOR Operation In CBC
XOR Is Central To CBC.
The XOR Operation Compares Corresponding Bits Of Two Values.
Its Basic Rules Are:
0 XOR 0 = 0
0 XOR 1 = 1
1 XOR 0 = 1
1 XOR 1 = 0
One Useful Property Is:
A ⊕ B ⊕ B = A
This Property Makes XOR Useful During Decryption.
Before Encryption, The Plaintext Block Is XORed With The Previous Ciphertext Block. During Decryption, The Decrypted Intermediate Value Is XORed With The Same Previous Ciphertext Block To Recover The Plaintext.
CBC Decryption
CBC Decryption Reverses The Encryption Process.
For The First Block:
P? = D?(C?) ⊕ IV
For Subsequent Blocks:
P? = D?(C?) ⊕ C???
where:
-
D? Represents Block-cipher Decryption Using Key K.
-
C? Is The Current Ciphertext Block.
-
C??? Is The Previous Ciphertext Block.
The Process Can Be Illustrated As:
C1 ---> AES Decryption ---> XOR ---> P1
                              ^
                              |
                             IV

C2 ---> AES Decryption ---> XOR ---> P2
                              ^
                              |
                             C1

C3 ---> AES Decryption ---> XOR ---> P3
                              ^
                              |
                             C2
Worked Conceptual Example
Consider A Message Divided Into Three Blocks:
P1
P2
P3
Let The IV Be:
IVCBC Encryption Works As Follows:
C1 = E(K, P1 XOR IV)

C2 = E(K, P2 XOR C1)

C3 = E(K, P3 XOR C2)
The Resulting Ciphertext Is:
C1 || C2 || C3During Decryption:
P1 = D(K, C1) XOR IV

P2 = D(K, C2) XOR C1

P3 = D(K, C3) XOR C2
This Demonstrates The Chaining Relationship Very Clearly.
CBC And Identical Plaintext Blocks
One Major Advantage Of CBC Over ECB Is That Identical Plaintext Blocks Do Not Necessarily Produce Identical Ciphertext Blocks.
Suppose:
P1 = P3In ECB Mode:
E(K,P1) = E(K,P3)Therefore:
C1 = C3But In CBC:
C1 = E(K,P1 XOR IV)while:
C3 = E(K,P3 XOR C2)Even Though P1 And P3 Are Identical, The Values Being Encrypted Are Different Because The Chaining Inputs Are Different.
Consequently:
C1 ≠ C3under Normal Circumstances.
This Helps Conceal Repeated Patterns In Plaintext.
Padding In CBC
Block Ciphers Require Complete Blocks. Suppose AES Uses 128-bit Blocks, But The Message Length Is Not An Exact Multiple Of 128 Bits.
Padding Is Therefore Required.
A Common Padding Scheme Is PKCS#7 Padding.
For Example, Suppose A Block Requires Four Additional Bytes. Four Bytes Containing The Value 04 Are Added.
Conceptually:
Original:
DATA DATA DATA

After Padding:
DATA DATA DATA 04 04 04 04
The Exact Representation Depends On The Block Size And The Amount Of Padding Required.
During Decryption, The Receiver Removes The Padding After Recovering The Plaintext.
Padding Must Be Validated Carefully Because Incorrect Padding Handling Can Create Security Vulnerabilities.
Error Propagation In CBC
CBC Has An Interesting Error-propagation Characteristic.
Suppose One Bit Of Ciphertext Block C? Is Modified.
During Decryption:
P? = D(C?) XOR C???Changing C? Generally Causes The Entire Decrypted Block P? To Become Unpredictable.
However, The Modified C? Is Also Used In The Decryption Of The Next Block:
P??? = D(C???) XOR C?Therefore, The Change Causes A Predictable Bit-level Alteration In The Corresponding Position Of P???.
After That, Subsequent Blocks Can Decrypt Normally.
Thus, A Ciphertext Modification Typically Affects two Plaintext Blocks In CBC Decryption.
CBC Does Not Provide Authentication
An Extremely Important Limitation Of CBC Is That encryption Alone Does Not Provide Message Authentication Or Integrity Protection.
CBC Can Provide Confidentiality, But An Attacker May Modify Ciphertext Without Knowing The Encryption Key.
This Means That CBC Should Generally Not Be Treated As An Authenticated-encryption Mechanism.
Modern Applications Should Prefer Authenticated Encryption Schemes Such As:
-
AES-GCM
-
ChaCha20-Poly1305
where Appropriate.
If CBC Must Be Used, It Should Normally Be Combined With A Secure Message Authentication Mechanism, Commonly Using An Encrypt-then-MAC Construction With Carefully Designed Keys And Verification Procedures.
Padding Oracle Attacks
One Of The Most Famous CBC Vulnerabilities Is The padding Oracle Attack.
A Padding Oracle Occurs When An Application Reveals, Directly Or Indirectly, Whether Decrypted Ciphertext Has Valid Padding.
An Attacker Can Submit Modified Ciphertext And Observe Differences In Application Behavior, Such As:
-
Different Error Messages
-
Different HTTP Status Codes
-
Different Response Times
-
Different Application Behavior
These Differences Can Allow An Attacker To Infer Plaintext Information.
Historical Examples Include Vulnerabilities Involving CBC-based Encryption In Protocols And Web Applications.
The Lesson Is Important: CBC Encryption Must Be Implemented With Authentication And Careful Error Handling.
CBC Security Considerations
A Secure CBC Implementation Requires More Than Simply Calling An Encryption Function.
Important Considerations Include:
-
Use A Strong Modern Block Cipher Such As AES.
-
Use A Sufficiently Strong Encryption Key.
-
Generate A Fresh, Unpredictable IV.
-
Never Use A Constant IV With CBC.
-
Avoid IV Reuse With The Same Key.
-
Authenticate Ciphertext.
-
Validate Padding Safely.
-
Avoid Distinguishable Error Messages.
-
Use Well-tested Cryptographic Libraries.
-
Prefer Authenticated Encryption When Possible.
These Requirements Are Particularly Important In Security-sensitive Applications.
CBC Compared With ECB
CBC Is Substantially Safer Than ECB For General Message Encryption.
| Feature | ECB | CBC |
|---|---|---|
| Chaining | No | Yes |
| IV | No | Yes |
| Repeated Blocks | Reveal Patterns | Concealed Better |
| Parallel Encryption | Yes | Generally No |
| Parallel Decryption | Yes | Yes |
| Authentication | No | No |
| Padding Required | Usually | Usually |
| Modern Recommendation | Generally Avoid | Legacy/use-case Dependent |
ECB Should Generally Not Be Used For Encrypting Structured Sensitive Data Because It Exposes Patterns.
CBC Improves Confidentiality But Still Lacks Authentication.
CBC Compared With CTR
CBC And Counter (CTR) Mode Operate Differently.
CBC Requires Plaintext Blocks To Be Processed Sequentially During Encryption Because Each Block Depends On The Previous Ciphertext.
CTR Mode Transforms A Block Cipher Into A Stream-like Construction Using A Counter.
CTR Encryption Can Be Expressed Conceptually As:
C? = P? ⊕ E?(Counter?)
CTR Has The Advantage Of Supporting Parallel Encryption And Random Access More Naturally.
However, CTR Also Does Not Inherently Provide Authentication.
CBC Compared With GCM
AES-CBC And AES-GCM Are Both Associated With AES But Provide Different Security Properties.
AES-CBC Primarily Provides Confidentiality.
AES-GCM Provides:
-
Confidentiality
-
Integrity
-
Authentication
GCM Is An Authenticated Encryption With Associated Data (AEAD) Mode.
Therefore, For Many Modern Applications, AES-GCM Is Preferable To Implementing AES-CBC Together With A Separate Authentication Mechanism.
Advantages Of CBC
CBC Has Several Advantages.
1. Pattern Concealment
CBC Hides Repeated Plaintext Patterns Better Than ECB.
2. Wide Historical Support
CBC Has Been Implemented In Numerous Cryptographic Libraries, Protocols, And Systems.
3. Simple Conceptual Structure
The Encryption And Decryption Equations Are Relatively Straightforward.
4. Compatibility
CBC Is Supported By Many Legacy Systems.
5. Strong Confidentiality When Correctly Implemented
With A Secure Block Cipher, Appropriate IV Handling, And Proper Cryptographic Construction, CBC Can Provide Strong Confidentiality.
Disadvantages Of CBC
CBC Also Has Significant Limitations.
1. No Built-in Authentication
CBC Does Not Automatically Protect Message Integrity.
2. Sequential Encryption
CBC Encryption Cannot Generally Process Blocks Independently Because Each Block Depends On The Previous Ciphertext Block.
3. Padding Requirements
Messages That Are Not Aligned To The Block Size Require Padding.
4. Padding Oracle Vulnerabilities
Poor Implementations Can Become Vulnerable To Padding Oracle Attacks.
5. Error Propagation
Ciphertext Corruption Can Affect Multiple Plaintext Blocks.
6. More Complex Secure Deployment
A Secure CBC System Requires Careful IV Generation, Authentication, Padding Validation, And Error Handling.
Applications Of CBC
CBC Has Historically Been Used In Many Areas Of Information Security.
Examples Include:
-
File Encryption
-
Database Encryption
-
Disk And Storage Encryption Components
-
Secure Communication Protocols
-
Legacy TLS Configurations
-
VPN Technologies
-
Secure Document Systems
-
Enterprise Encryption Applications
-
Cryptographic Libraries
-
Embedded Security Systems
However, Whether CBC Should Be Used In A New System Depends Heavily On The Application's Security Requirements And Available Cryptographic Primitives.
CBC In Network Security
CBC Has Historically Appeared In Network Security Protocols.
For Example, Earlier Versions And Cipher-suite Configurations Of TLS Used CBC-based Encryption.
CBC Introduced Additional Complexities In Network Protocols Because Attackers Could Exploit Implementation Details, Padding Behavior, Timing Differences, And Message Processing Characteristics.
This Contributed To The Preference For Authenticated Encryption Modes In Newer Protocol Designs.
Modern Secure Protocol Implementations Generally Favor AEAD Algorithms Rather Than Manually Combining CBC Encryption With Separate Integrity Mechanisms.
CBC In File Encryption
CBC Can Be Used For Encrypting Files By Dividing The File Into Blocks.
For Example:
File
 |
 +-- Block 1
 +-- Block 2
 +-- Block 3
 +-- Block 4
 |
CBC Encryption
 |
 +-- C1
 +-- C2
 +-- C3
 +-- C4
However, A Secure File-encryption Design Should Also Protect The Ciphertext Against Unauthorized Modification.
Therefore, Simply Encrypting A File Using AES-CBC Is Insufficient For A Robust Modern File-encryption System. Authentication, Key Management, Metadata Protection, And Secure IV Generation Are Also Important.
CBC And Key Management
The Security Of CBC Ultimately Depends On The Security Of The Cryptographic Key.
If An Attacker Obtains The Key, CBC Confidentiality Is Compromised.
Therefore, Applications Should Use Appropriate Key-management Practices, Including:
-
Strong Random Key Generation
-
Secure Key Storage
-
Key Rotation
-
Access Control
-
Hardware-backed Key Storage Where Appropriate
-
Separation Of Encryption And Authentication Keys
-
Secure Key Destruction
Passwords Should Not Normally Be Used Directly As AES Keys. A Password-based Key Derivation Function Such As Argon2id, scrypt, Or PBKDF2 Should Be Used Where Passwords Are Involved.
CBC And Confidentiality
CBC's Main Security Objective Is Confidentiality.
A Properly Constructed CBC Encryption System Prevents An Unauthorized Party From Directly Recovering Plaintext From Ciphertext.
However, Confidentiality Depends On Several Factors:
Strong Cipher
      +
Strong Key
      +
Secure IV
      +
Correct CBC Implementation
      +
Secure Authentication
      =
Secure Encryption System
A Weakness In Any One Of These Components Can Compromise The Overall System.
CBC Mathematical Representation
The Complete CBC Encryption Process Can Be Represented Mathematically As:
C? = E?(P? ⊕ IV)
For:
i = 2, 3, ..., N
we Have:
C? = E?(P? ⊕ C???)
The Decryption Equations Are:
P? = D?(C?) ⊕ IV
and:
P? = D?(C?) ⊕ C???
These Equations Define The Essential Behavior Of CBC.
CBC Encryption Flow
A Complete CBC Encryption Workflow Is:
Plaintext
   |
   V
Divide Into Blocks
   |
   V
Add Padding If Necessary
   |
   V
Generate Secure IV
   |
   V
P1 XOR IV
   |
   V
Block Cipher Encryption
   |
   V
C1
   |
   +------+
          |
P2 XOR C1
   |
   V
Block Cipher Encryption
   |
   V
C2
   |
   +------+
          |
P3 XOR C2
   |
   V
Block Cipher Encryption
   |
   V
C3
The Ciphertext And IV Can Then Be Stored Or Transmitted According To The Application's Secure Protocol.
Why CBC Is Important For Cryptography Students?
CBC Is An Important Topic In Cryptography Because It Demonstrates How A Basic Block Cipher Can Be Transformed Into A Mechanism For Encrypting Arbitrary-length Messages.
It Also Introduces Several Fundamental Cryptographic Concepts:
-
Initialization Vectors
-
XOR Operations
-
Chaining
-
Block Padding
-
Error Propagation
-
Confidentiality
-
Integrity
-
Authentication
-
Cryptographic Implementation Risks
Understanding CBC Also Makes It Easier To Understand Other Modes Such As ECB, CFB, OFB, CTR, And GCM.
CBC In Modern Cryptography
CBC Remains Academically Important And Is Still Encountered In Legacy Systems, But It Is No Longer The Default Choice For Many New Applications.
Modern Cryptographic Engineering Emphasizes authenticated Encryption.
Rather Than Designing:
Encryption
+
Separate Authentication
modern Applications Often Use:
Authenticated Encryption
        |
        +-- Confidentiality
        |
        +-- Integrity
        |
        +-- Authentication
AES-GCM And ChaCha20-Poly1305 Are Common Examples.
Nevertheless, Understanding CBC Remains Essential For Cybersecurity Professionals Because Legacy Applications, Protocols, Vulnerabilities, And Forensic Investigations May Still Involve CBC.
Conclusion
Cipher Block Chaining Is A Foundational Block-cipher Mode That Connects Consecutive Plaintext Blocks Through Ciphertext Feedback. The First Plaintext Block Is XORed With An Initialization Vector, While Every Subsequent Plaintext Block Is XORed With The Previous Ciphertext Block Before Encryption.
CBC Significantly Improves Upon ECB By Preventing Identical Plaintext Blocks From Automatically Producing Identical Ciphertext Blocks. It Has Historically Been Used With Algorithms Such As DES And AES In Numerous Security Applications.
However, CBC Has Important Limitations. It Does Not Inherently Provide Authentication Or Integrity, Requires Careful Padding Management, And Can Be Vulnerable To Padding-oracle Attacks When Implemented Incorrectly. Encryption Is Also Sequential, Which Can Reduce Performance Compared With Highly Parallelizable Modes.
For Modern System Design, Authenticated-encryption Modes Such As AES-GCM Or ChaCha20-Poly1305 Are Generally Preferable Where Supported. Nevertheless, CBC Remains An Important PG/M.Tech/PhD-level Cryptography Concept Because It Provides A Clear Foundation For Understanding Block-cipher Modes, Initialization Vectors, Chaining, Padding, Error Propagation, And The Distinction Between Confidentiality And Authentication.
Tags:
Cipher Block Chaining (CBC), Cipher Block Chaining, Definition Of Cipher Block Chaining, Cryptography Concept